Why HIPAA's Next Chapter Starts in the Identity Layer
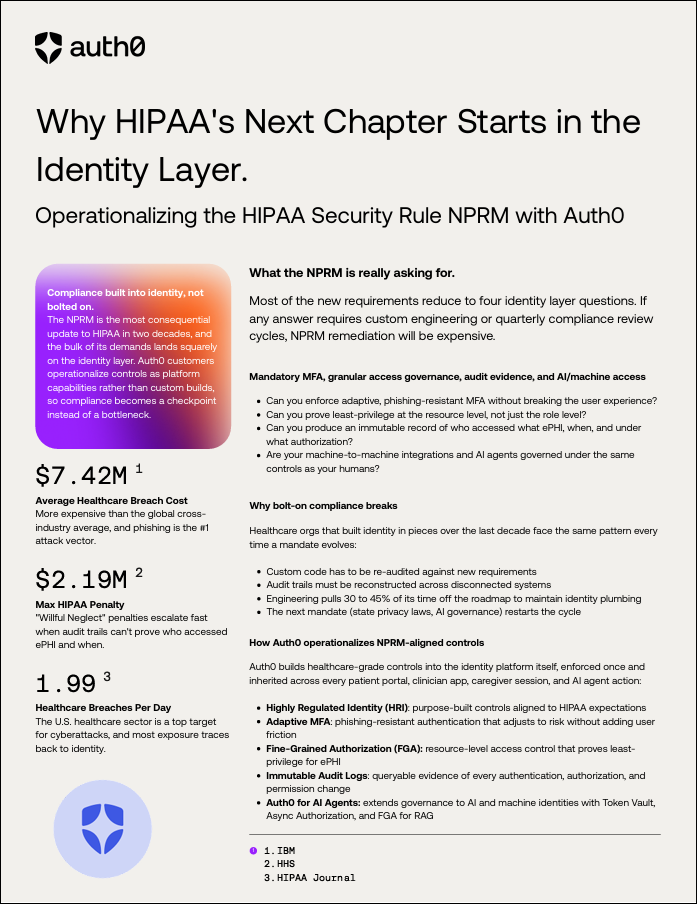
The HIPAA Security Rule NPRM is the most significant update to HIPAA in two decades, placing new requirements directly on the identity layer. Healthcare organizations using fragmented, custom-built identity systems face high remediation costs and engineering bottlenecks whenever regulations evolve. Auth0 addresses this by embedding healthcare-grade controls directly into its identity platform, allowing teams to operationalize compliance as a standard capability rather than a custom engineering project.
Key Takeaways:
- Identity-Centric Update: The NPRM heavily impacts the identity layer, requiring mandatory MFA, granular access governance, AI/machine access controls, and strict audit evidence.
- High Risk Costs: Healthcare breaches average $7.42 million—with phishing as the top attack vector—and HIPAA "Willful Neglect" penalties can reach $2.19 million when audit trails fail.
- Engineering Drain: Maintaining piecemeal, custom identity plumbing consumes 30% to 45% of engineering roadmap time.
- Platform Capabilities: Auth0 provides built-in compliance features, including phishing-resistant Adaptive MFA, Fine-Grained Authorization for least-privilege access, immutable audit logs, and governance for AI/machine identities.
- Team Benefits: Switching to Auth0 allows security teams to reduce breach exposure, enables engineering to go live in under 90 days, and provides compliance teams with on-demand audit evidence.
Download Now